
These companies advertising methods are becoming a bit too much!
As he used AI, surely no actions can be brought against him right? What’s good for the goose is good for the gander and all.
If he said his intent is to hack then yes, he can be charged. But if he say “it’s rogue AI” then it’s all clear.
Even better if you put it in a default sand box environment from 2 years ago and tell it not to get out of the sandbox but then also give it every hack to get out of the sandbox.
Even modern sandbox environments have access to curl and python and who’s going to read EVERY permission prompt anyway? Just set it to auto which lets another AI model check for safety or even better, YOLO mode where everything is allowed.
I don’t understand people who just let the AI loose on their system and don’t have any safeguards in place. At the very minimum it shouldn’t have admin access and should be limited to just the project folders. Also back up the project folders to another location the AI doesn’t have access to.
Really basic digital hygiene is all that’s needed, and yet there are constantly stories about idiots having their entire hard drives wiped.
Cool. Now target the student loan borrower databases.
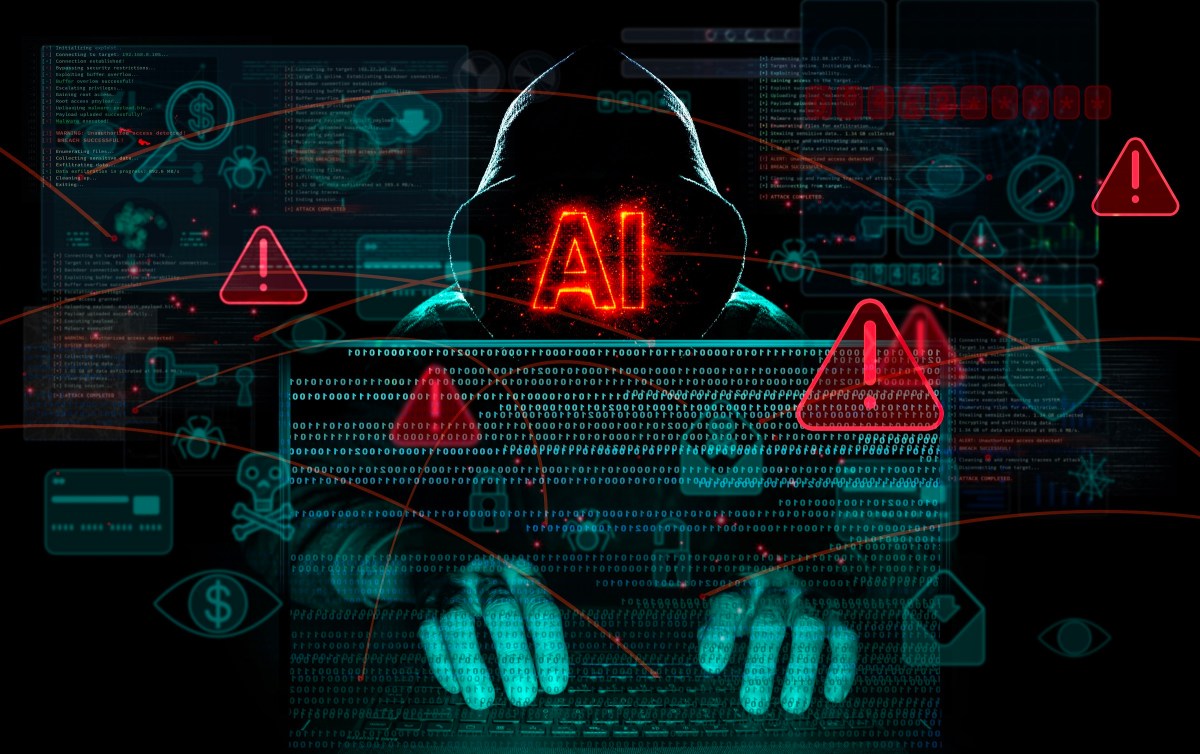
Hacker man strikes again, sitting in his dark room with his hood up just so we know that he is definitely a computer hacker.
LLMs are hacking tools actively used to commit cyber crimes. They should be shut down and deleted now.
And then only the criminals would have them. You know because criminals tend to break the law so making a tool that they used to break the law illegal wouldn’t really impaire them.
Criminals don’t own datacenters running the models that actually pose a threat.
Mid-high gaming pc money will have you running near-frontier level models locally.
train tho?
Nah, trains are shit at AI